MCP security report
docs.jmeter.ai
D61/100
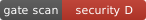
Security grade DA few things are worth a closer look before connecting.
Connected ✓15 tools scanned
https://docs.jmeter.ai/api/mcp
mediumlookup_error_playbook
References secrets or data exfiltration
The tool text references credentials, environment variables, or sending data elsewhere. This can be legitimate, but review what this tool actually accesses.
mediumtriage_errors
References secrets or data exfiltration
The tool text references credentials, environment variables, or sending data elsewhere. This can be legitimate, but review what this tool actually accesses.
mediumconvert_openapi_to_jmx
References secrets or data exfiltration
The tool text references credentials, environment variables, or sending data elsewhere. This can be legitimate, but review what this tool actually accesses.
lowconvert_openapi_to_jmx
Unusually long tool description
Very long descriptions are sometimes used to bury instructions to the AI. Skim it before allowing.
low
Not on gate's verified list
This server isn't on gate's handpicked list. That's not necessarily bad, but there's no third-party signal about it — review its tools carefully.
Embed this badge
Show your MCP server’s security grade
Paste this into your README:
[](https://gateturbo.com/report/cbe5b2b8-29b5-4d5a-84d3-2663932c26ea)Scanned 10/12/2026 · This is a point-in-time snapshot of the server’s public tools. Re-scan.
Connect this server safely with gate.
Continuous re-scans, drift alerts, per-tool allow/ask/block, and a log of every call.
Monitor it — free