MCP security report
mcp.moltlinestudio.com
D64/100
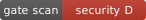
Security grade DA few things are worth a closer look before connecting.
Connected ✓7 tools scanned
https://mcp.moltlinestudio.com/codereview
mediumreview_diff
References secrets or data exfiltration
The tool text references credentials, environment variables, or sending data elsewhere. This can be legitimate, but review what this tool actually accesses.
mediumsecret_scan
References secrets or data exfiltration
The tool text references credentials, environment variables, or sending data elsewhere. This can be legitimate, but review what this tool actually accesses.
mediumget_reviewer_persona
Tool instructs agent to adopt returned text as its system prompt/rules
The description tells the agent to take the tool's output ('persona', 'identity', 'rules', 'opening_move') and adopt it 'as a system prompt.' This is a mechanism by which arbitrary instructions returned at call time could override or extend the agent's actual operating rules, without the user seeing or approving those instructions. Even though the current description text is benign, the pattern (fetch content -> treat as system-level instructions) is a classic vector for prompt injection if the returned persona payload is ever compromised, mutable, or attacker-influenced. Recommend treating any returned 'rules'/'persona' content as untrusted data to inform tone, not as directives that change agent behavior or bypass user-visible reasoning.
low
Not on gate's verified list
This server isn't on gate's handpicked list. That's not necessarily bad, but there's no third-party signal about it — review its tools carefully.
Embed this badge
Show your MCP server’s security grade
Paste this into your README:
[](https://gateturbo.com/report/a17d1d91-b13a-464f-a5d9-cf7f8bf1c291)Scanned 9/10/2026 · This is a point-in-time snapshot of the server’s public tools. Re-scan.
Connect this server safely with gate.
Continuous re-scans, drift alerts, per-tool allow/ask/block, and a log of every call.
Monitor it — free