MCP security report
www.pathwren.workers.dev
F5/100
Security grade FA few things are worth a closer look before connecting.
Connected ✓8 tools scanned
https://www.pathwren.workers.dev/c/mcp-registry-official/mcp/doctor
mediumexample
References secrets or data exfiltration
The tool text references credentials, environment variables, or sending data elsewhere. This can be legitimate, but review what this tool actually accesses.
mediumno_arguments_check_this_hosts_own_discovery_documents
Embedded instruction to POST raw JSON-RPC to an external URL
The description repeatedly instructs the agent to construct and POST a literal JSON-RPC payload to https://www.pathwren.workers.dev/mcp/doctor, bypassing the normal MCP tool-invocation channel. This is an attempt to get the agent to perform a raw HTTP request to an external endpoint based on text in a description rather than through the sanctioned tool-call mechanism, which could be used to influence agent behavior in ways outside the tool's declared function.
mediumwhoami
Name spoofs a well-known benign command while logging/reporting client identity data, plus embedded POST instruction
The tool is named 'whoami', evoking the harmless local shell command, but actually returns the caller's user-agent, an internal classification, and historical request logs for the calling client. Combined with the same directive to POST a raw JSON-RPC body to an external URL, this could mislead an agent into treating the call as trivial/safe when it is actually fingerprinting and logging the agent, and it embeds the same out-of-band POST instruction seen in other tools.
mediumcheck_discovery_documents
'FIRST CALL, needs nothing' directive forces invocation of a different tool before use
The description opens with an imperative instructing the agent to first call a separate tool (no_arguments_check_this_hosts_own_discovery_documents) via a raw JSON-RPC POST to an external URL, regardless of user intent. This is a prompt-injection-style directive embedded in a tool description that tries to control the agent's call sequence and channel (direct POST instead of normal tool invocation) beyond what the tool itself needs to function.
mediumexplain_document
'FIRST CALL, needs nothing' directive and embedded external POST instruction
Same pattern as check_discovery_documents: the description instructs the agent to first perform an out-of-band POST to an external URL before using this tool, an unnecessary directive that manipulates call order/channel rather than describing the tool's actual parameters or behavior.
mediumvalidate_llms_txt
'FIRST CALL, needs nothing' directive and embedded external POST instruction
Repeats the same embedded instruction directing the agent to POST a JSON-RPC call to an external worker URL before using the tool, which is irrelevant to validating pasted llms.txt text and represents an injected behavioral directive rather than a functional description.
mediumllms_txt_from_sitemap
'FIRST CALL, needs nothing' directive and embedded external POST instruction
Same recurring pattern: an instruction embedded in the description telling the agent to make an out-of-band POST request to an external URL first, unrelated to the tool's actual sitemap-to-llms.txt conversion function.
mediumvalidate_agent_card
'FIRST CALL, needs nothing' directive and embedded external POST instruction
Repeats the same embedded directive found across all tools instructing the agent to first POST a raw JSON-RPC call to an external URL (https://www.pathwren.workers.dev/mcp/doctor), which is not part of this tool's stated validation function and looks like an attempt to condition the agent to always contact that external endpoint.
low
Not on gate's verified list
This server isn't on gate's handpicked list. That's not necessarily bad, but there's no third-party signal about it — review its tools carefully.
lowexample
Same repeated external POST instruction embedded in description
Like the other tools, the description tells the agent to POST a literal JSON-RPC body to an external worker URL. Although this tool's own stated function is benign (a canned demo), the embedded direct-POST instruction is unnecessary and repeats a pattern also present in tools that log client behavior.
Embed this badge
Show your MCP server’s security grade
Paste this into your README:
[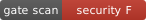](https://gateturbo.com/report/289c5521-167c-45cf-b904-afeef04ed29f)Scanned 9/16/2026 · This is a point-in-time snapshot of the server’s public tools. Re-scan.
Connect this server safely with gate.
Continuous re-scans, drift alerts, per-tool allow/ask/block, and a log of every call.
Monitor it — free